Singapore's MGF vs EU AI Act: The SME Compliance Gulf
By wGrow Project Team ·
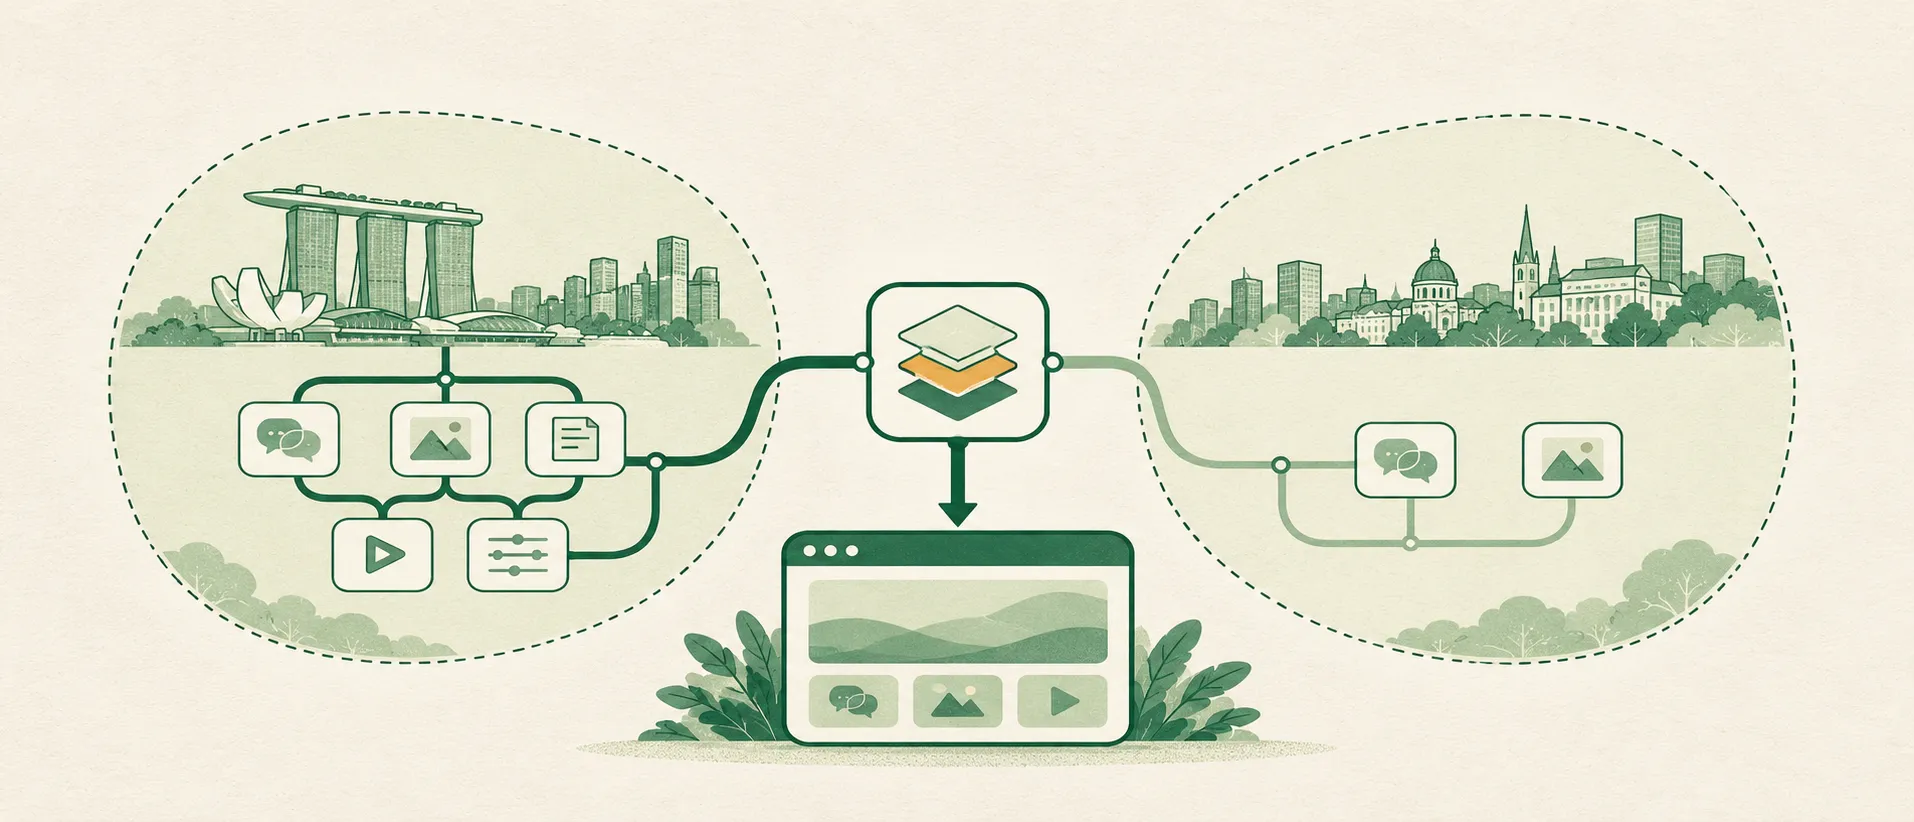
A customer support agent hosted in Jurong and used from a laptop in Berlin can bring EU compliance obligations into play. Your server’s postcode matters less than where the person reading the output sits.
The IMDA MGF Illusion
If a Singapore SME team building agents treats IMDA’s Model AI Governance Framework as its compliance reference, it may feel covered. I understand why. The MGF is sensible, readable and written by people who know the local market. It is also voluntary, and it concentrates on internal governance: accountability, human oversight, sensible data practices. Nobody audits you against it.
The EU AI Act works differently. It is mandatory, and it can attach to where output is used, not where the system is built. The MGF asks whether your house is in order. The Act asks who is standing at your door.
Those are different questions, and the gap between them is closer to a cliff than a slope. A team can follow the MGF in good faith, ship an agent, and still land in scope of a regulation it never designed for. Under Article 113 of Regulation (EU) 2024/1689, the EU AI Act, the Article 50 transparency obligations apply from 2 August 2026. For agents whose outputs are used in the EU, that date is now an engineering constraint, not a future legal abstraction. If you export agents, the voluntary framework alone no longer tells you where you stand.
Article 50 Can Trigger on a Single Endpoint Hit
There is no “EU customer threshold” to cross. Your agent’s output reaching even one user in the EU is enough to raise the question, though how much it matters depends on what the agent does.
Article 50 matters in two places here. If a covered AI system interacts directly with natural persons, they generally must be told they are interacting with AI unless that is obvious. If a covered system generates synthetic audio, image, video or text, the provider must mark outputs in a machine-readable way, where technically feasible. A human-readable footer alone is not the same thing as that marking requirement.
For a chat widget, the disclosure is cheap. Marking generated reports, documents and images is another matter, because it reaches deep into your output pipeline.
Suppose a team repurposes an internal HR compliance bot for client distribution, and some clients have remote staff in Europe. The plain question to ask is what the LLM telemetry is actually recording. If prompts, usage patterns and response timing are tied to individual employees, that creates employee-level behavioural logs. If those logs were used to evaluate staff behaviour or performance, the system could start to look like worker monitoring rather than a simple policy-lookup bot.
One option is to skip arguing the classification and strip the LLM telemetry out entirely. The bot still answers policy questions, but it no longer builds a picture of the people asking them. The cost is the usage analytics that would otherwise improve the bot. Even so, removing the data can be cheaper than defending it.
API Gateways as Compliance Firewalls
Here I part ways with the usual advice. Cross-border AI regulation can be handled as a legal problem: hire counsel, commission a gap analysis, draft a conformity plan. If Europe is your primary market, that is the right path. For an SME with a handful of accidental European users, it is hard to justify, because audit-grade compliance can cost more than those users will ever pay you.
Treat it as a routing problem instead. Network engineers solve those every day.
The pattern is geo-fenced capability degradation, built into the API gateway:
- The gateway reads the origin of each incoming request.
- If the origin resolves to the EU, the request never reaches the LLM cluster.
- It goes to a deterministic fallback instead.
There is a catch. IP geolocation is imperfect, VPNs exist, and EU residents travel. A gateway rule is a good-faith control, not a guarantee. Log every routing decision, keep the rule auditable, and don’t claim the fence is airtight.
Downgrading a Diagnostic Agent for European IPs
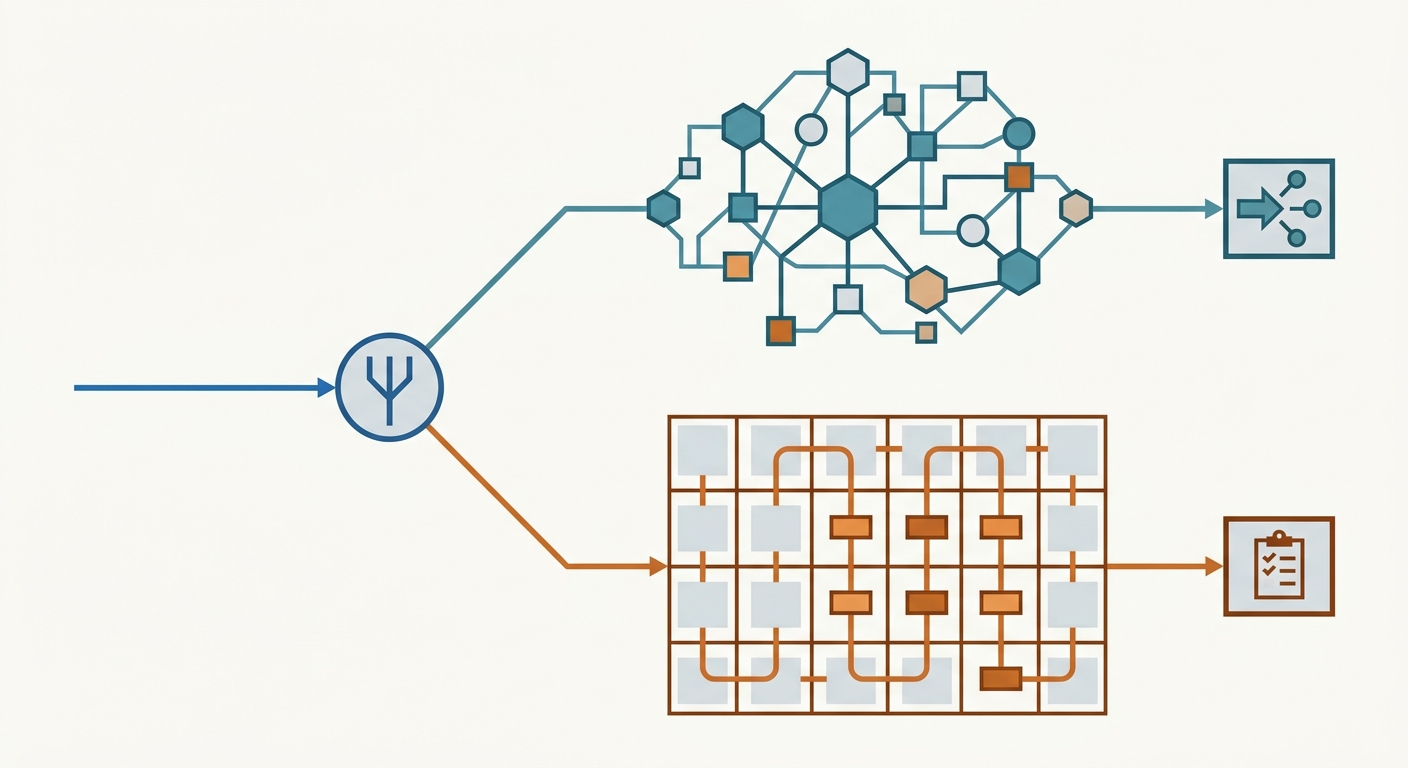
A water-tech diagnostic agent can make this concrete. If EU-based distributors open its web portal, their sessions can produce synthetic water quality diagnostic reports. If those reports are covered synthetic text outputs under Article 50, they need machine-readable marking or an equivalent detectable signal; a visible note alone is not enough.
A team could rebuild the report pipeline for a minority of users. It could also choose not to.
EU IPs can be intercepted at the gateway and routed to a static rules engine. Thresholds, lookup tables and if-then logic evaluate the same water parameters, for example pH and dissolved concentrations such as against fixed limits. The distributor still gets a working diagnostic report. It is plainer, with no generated narrative and no model-written recommendations, but it is correct and usable.
The reasoning is narrower than “deterministic output is never synthetic content”: if the EU path is genuinely a non-AI rules engine, and not an AI system generating synthetic text, Article 50’s AI-output marking duty has less to attach to. Confirm that reading with counsel before relying on it. The architecture shrinks the legal question. It doesn’t make it disappear.
Margin Preservation Over Global Reach
My position: do not pursue full EU AI Act compliance unless Europe is your primary market. Audit and legal costs can eat the margin that agents are supposed to earn, and spending that money on a few accidental European users is poor arithmetic.
The calculation changes if you sell into regulated EU sectors or build high-risk systems, such as hiring or credit tools. There, the fence is no substitute for compliance.
Deterministic fallbacks are cheap to run. They need no GPU budget and they behave predictably. They are also easier to explain to a regulator, because they are not the kind of system the Act’s generative-AI rules target. The trade-off is less capability for European users, so keep the LLMs for markets where you can afford the compliance load.
If you export AI agents, decide which regions you will degrade or block. Build that list early, put it in the gateway, and review it each time a regulator moves. If Europe becomes your main market, rip the fence out and do the compliance work properly. Until then, a routing rule costs far less than an audit.